Let's talk about the AI arms race happening in business right now.
Everywhere you turn, someone's telling you that if you're not using AI, you're falling behind. AI agents. AI employees. AI-powered CRMs. AI-generated marketing. AI-powered everything.
Apparently, if a process exists, someone believes AI should be running it. And businesses are buying into it — not necessarily because they've identified a problem AI can solve, but because they've been convinced that everyone else is moving faster.
Here's something that might sound strange coming from someone who owns an AI and technology strategy consulting firm: your business probably doesn't need nearly as much AI as people are trying to sell you.
That doesn't mean AI isn't powerful. It means understanding what makes technology valuable requires more than understanding what it's capable of doing.
Being Early Isn't the Same as Being Strategic.
There's a difference between staying ahead of technology and chasing it.
I've built my career around understanding business operations, revenue generation, leadership, and how people actually work. And one thing that experience has taught me is that businesses rarely struggle because they don't have enough software.
They struggle because information doesn't move where it needs to go. Processes aren't clearly defined. Departments operate independently. Employees aren't trained properly. Or leadership doesn't have visibility into what's happening.
None of those problems automatically requires artificial intelligence. Yet somehow, AI has become the first recommendation instead of one of the options.
Before asking how to implement AI, I'd rather ask: what are we trying to accomplish, and what's preventing us from doing it today?
That question might lead us to AI. It might also lead us somewhere much simpler.
Not Every Automation Needs Intelligence.
One of the biggest misconceptions I'm seeing is the idea that automation and AI are interchangeable. They're not.
Traditional automation follows defined rules. When a particular event occurs, the system performs a predetermined action. AI can interpret information, generate content, recognize patterns, and support decisions in situations where rigid rules alone may not be sufficient.
Those capabilities can be valuable. But they also introduce different considerations around reliability, data access, monitoring, cost, and accountability.
Let's use a simple example. A business wants to automatically remind customers about outstanding estimates. Does that require an AI agent? Probably not. A CRM or workflow automation can often trigger a follow-up based on a defined schedule, update a record, and notify the responsible employee.
Now imagine that same business wants to analyze hundreds of unstructured customer inquiries, identify recurring themes, and help employees prepare tailored responses. AI might be worth evaluating.
The difference is the problem we're solving. If a predictable process can be handled reliably with a simple workflow, adding AI doesn't automatically make it better. Sometimes it just makes it more expensive and harder to maintain.
Your Broken Process Doesn't Become Brilliant Because AI Is Running It.
I've worked with businesses where the biggest opportunity wasn't introducing new technology — it was understanding how work moved through the organization.
In one commercial installation engagement, we evaluated customer inquiries, quoting, scheduling, field reporting, purchasing, and financial workflows. The business had multiple processes that needed better coordination. Rather than recommending AI agents to manage everything, we developed a phased strategy using existing Microsoft 365 capabilities, workflow automation, and targeted integrations.
Why? Because the business needed more consistent processes, clearer responsibilities, and better connections between the systems it already used. Adding AI to undefined workflows would not have resolved those underlying issues — it could have introduced additional complexity before the operational foundation was ready.
This is where a lot of technology conversations go wrong. Someone sees employees spending hours on manual work and immediately recommends AI. But nobody asks why the manual work exists. Is information being entered multiple times? Are approvals unclear? Are departments using disconnected systems? Are employees working around a process that no longer makes sense?
If you don't understand the source of the inefficiency, you risk automating the wrong thing. Automating a broken process doesn't fix the process. It just helps the problem move faster.
AI Agents Deserve More Questions Than They're Getting.
This is where I become particularly concerned about how AI is being marketed.
There's a significant difference between using AI to help draft an email and giving an AI agent permission to interact with financial systems, customer records, or operational platforms. An AI agent may be able to retrieve information, initiate workflows, update records, communicate with other systems, or perform actions on behalf of a business. That can create enormous opportunities. It can also create risks that business owners may not realize they're accepting.
I recently had a conversation at a networking event about a company developing AI agents for investment-related activities. As we discussed the concept, questions came up about security, liability, insurance, and what safeguards would exist around access to financial information. The conversation reinforced something I've been saying for a while: just because someone knows how to build an AI solution doesn't mean they've addressed everything required to operate it responsibly.
Before giving an AI system access to sensitive business information, I'd want answers to some fundamental questions. What information can it access? What actions can it take without human approval? How are permissions restricted? What happens when it produces an incorrect result? Who monitors its activity? Can its actions be reviewed or reversed? What happens if the vendor experiences a security incident? And who is accountable when something goes wrong?
These aren't questions designed to slow innovation. They're questions that help businesses adopt innovation without blindly accepting unnecessary exposure.
The Human Side Isn't Optional.
Another issue that doesn't get nearly enough attention is what happens to the people expected to use these systems.
I've spent years leading and developing teams, and I've learned that employees don't automatically embrace change because leadership announces that something will make their jobs easier. They need to understand what's changing, why it's changing, how their responsibilities will be affected, and what support they'll receive while learning something new.
AI introduces additional concerns. Employees may worry about job security, accuracy, monitoring, or whether they're expected to trust outputs they don't fully understand. Those concerns shouldn't be dismissed as resistance. They're part of the implementation strategy.
If leadership introduces AI without clear expectations, appropriate training, and accountability, the organization may end up with inconsistent usage, unnecessary workarounds, or employees relying on outputs they haven't been taught to verify.
A successful AI implementation isn't measured by how many employees have access to the tool. It's measured by whether the tool improves the work without creating unacceptable risks. Technology adoption is a human process. It always has been.
AI Readiness Is More Than Buying a License.
A company can purchase AI licenses tomorrow. That doesn't mean it's ready to use them effectively.
Before recommending AI, I want to understand the organization's operational foundation. Are its processes documented? Is its data accurate and accessible to the right people? Are security permissions appropriately configured? Does leadership understand what the proposed AI system will and won't do? Are there clear responsibilities for reviewing outputs and approving consequential actions? How will the business evaluate whether the investment is worthwhile? And perhaps most importantly, does the proposed use case actually require AI?
Sometimes the answer will be yes. AI can help businesses analyze large volumes of information, support employees working with unstructured data, accelerate research, and improve certain decision-support workflows. But those opportunities need to be evaluated against accuracy requirements, risk, cost, maintenance, and the business's ability to manage the technology.
A tool being available isn't a business case. And a demonstration isn't proof that the solution belongs inside your organization.
You Don't Need to Be First. You Need to Be Intentional.
I believe businesses should understand emerging technology. I believe leaders should be curious about AI and the opportunities it creates. And I believe organizations that refuse to evaluate new capabilities may miss meaningful opportunities.
But curiosity and urgency aren't the same thing. You can be forward-thinking without being reckless. You can experiment without giving a new system unrestricted access to your operations. You can invest in innovation without abandoning the processes, people, and safeguards that make your business function. And you can decide that a particular AI solution isn't right for your company today without deciding that AI has no place in your future.
Being ahead of the curve isn't about adopting everything first. It's about recognizing what's worth adopting before everyone else understands why. That's the difference between following a trend and developing a strategy.
At Jack-IT, AI is an option — not the starting point. We work with businesses to evaluate AI opportunities, identify appropriate use cases, improve workflows, connect systems, and prepare employees for technology adoption. But we also understand that AI isn't the answer to every business challenge. Sometimes the better investment is a properly configured CRM, a Microsoft 365 workflow, improved departmental communication, employee training, or clearer operational accountability. And sometimes AI genuinely is the right next step.
Our responsibility is to help businesses understand the difference — because the goal isn't to become the company using the most AI. It's to become the company making the smartest decisions about how technology supports its business.
Before You Add Another AI Tool, Ask What Problem It's Solving.
Jack-IT Consulting | Strategy Before Software. Always.
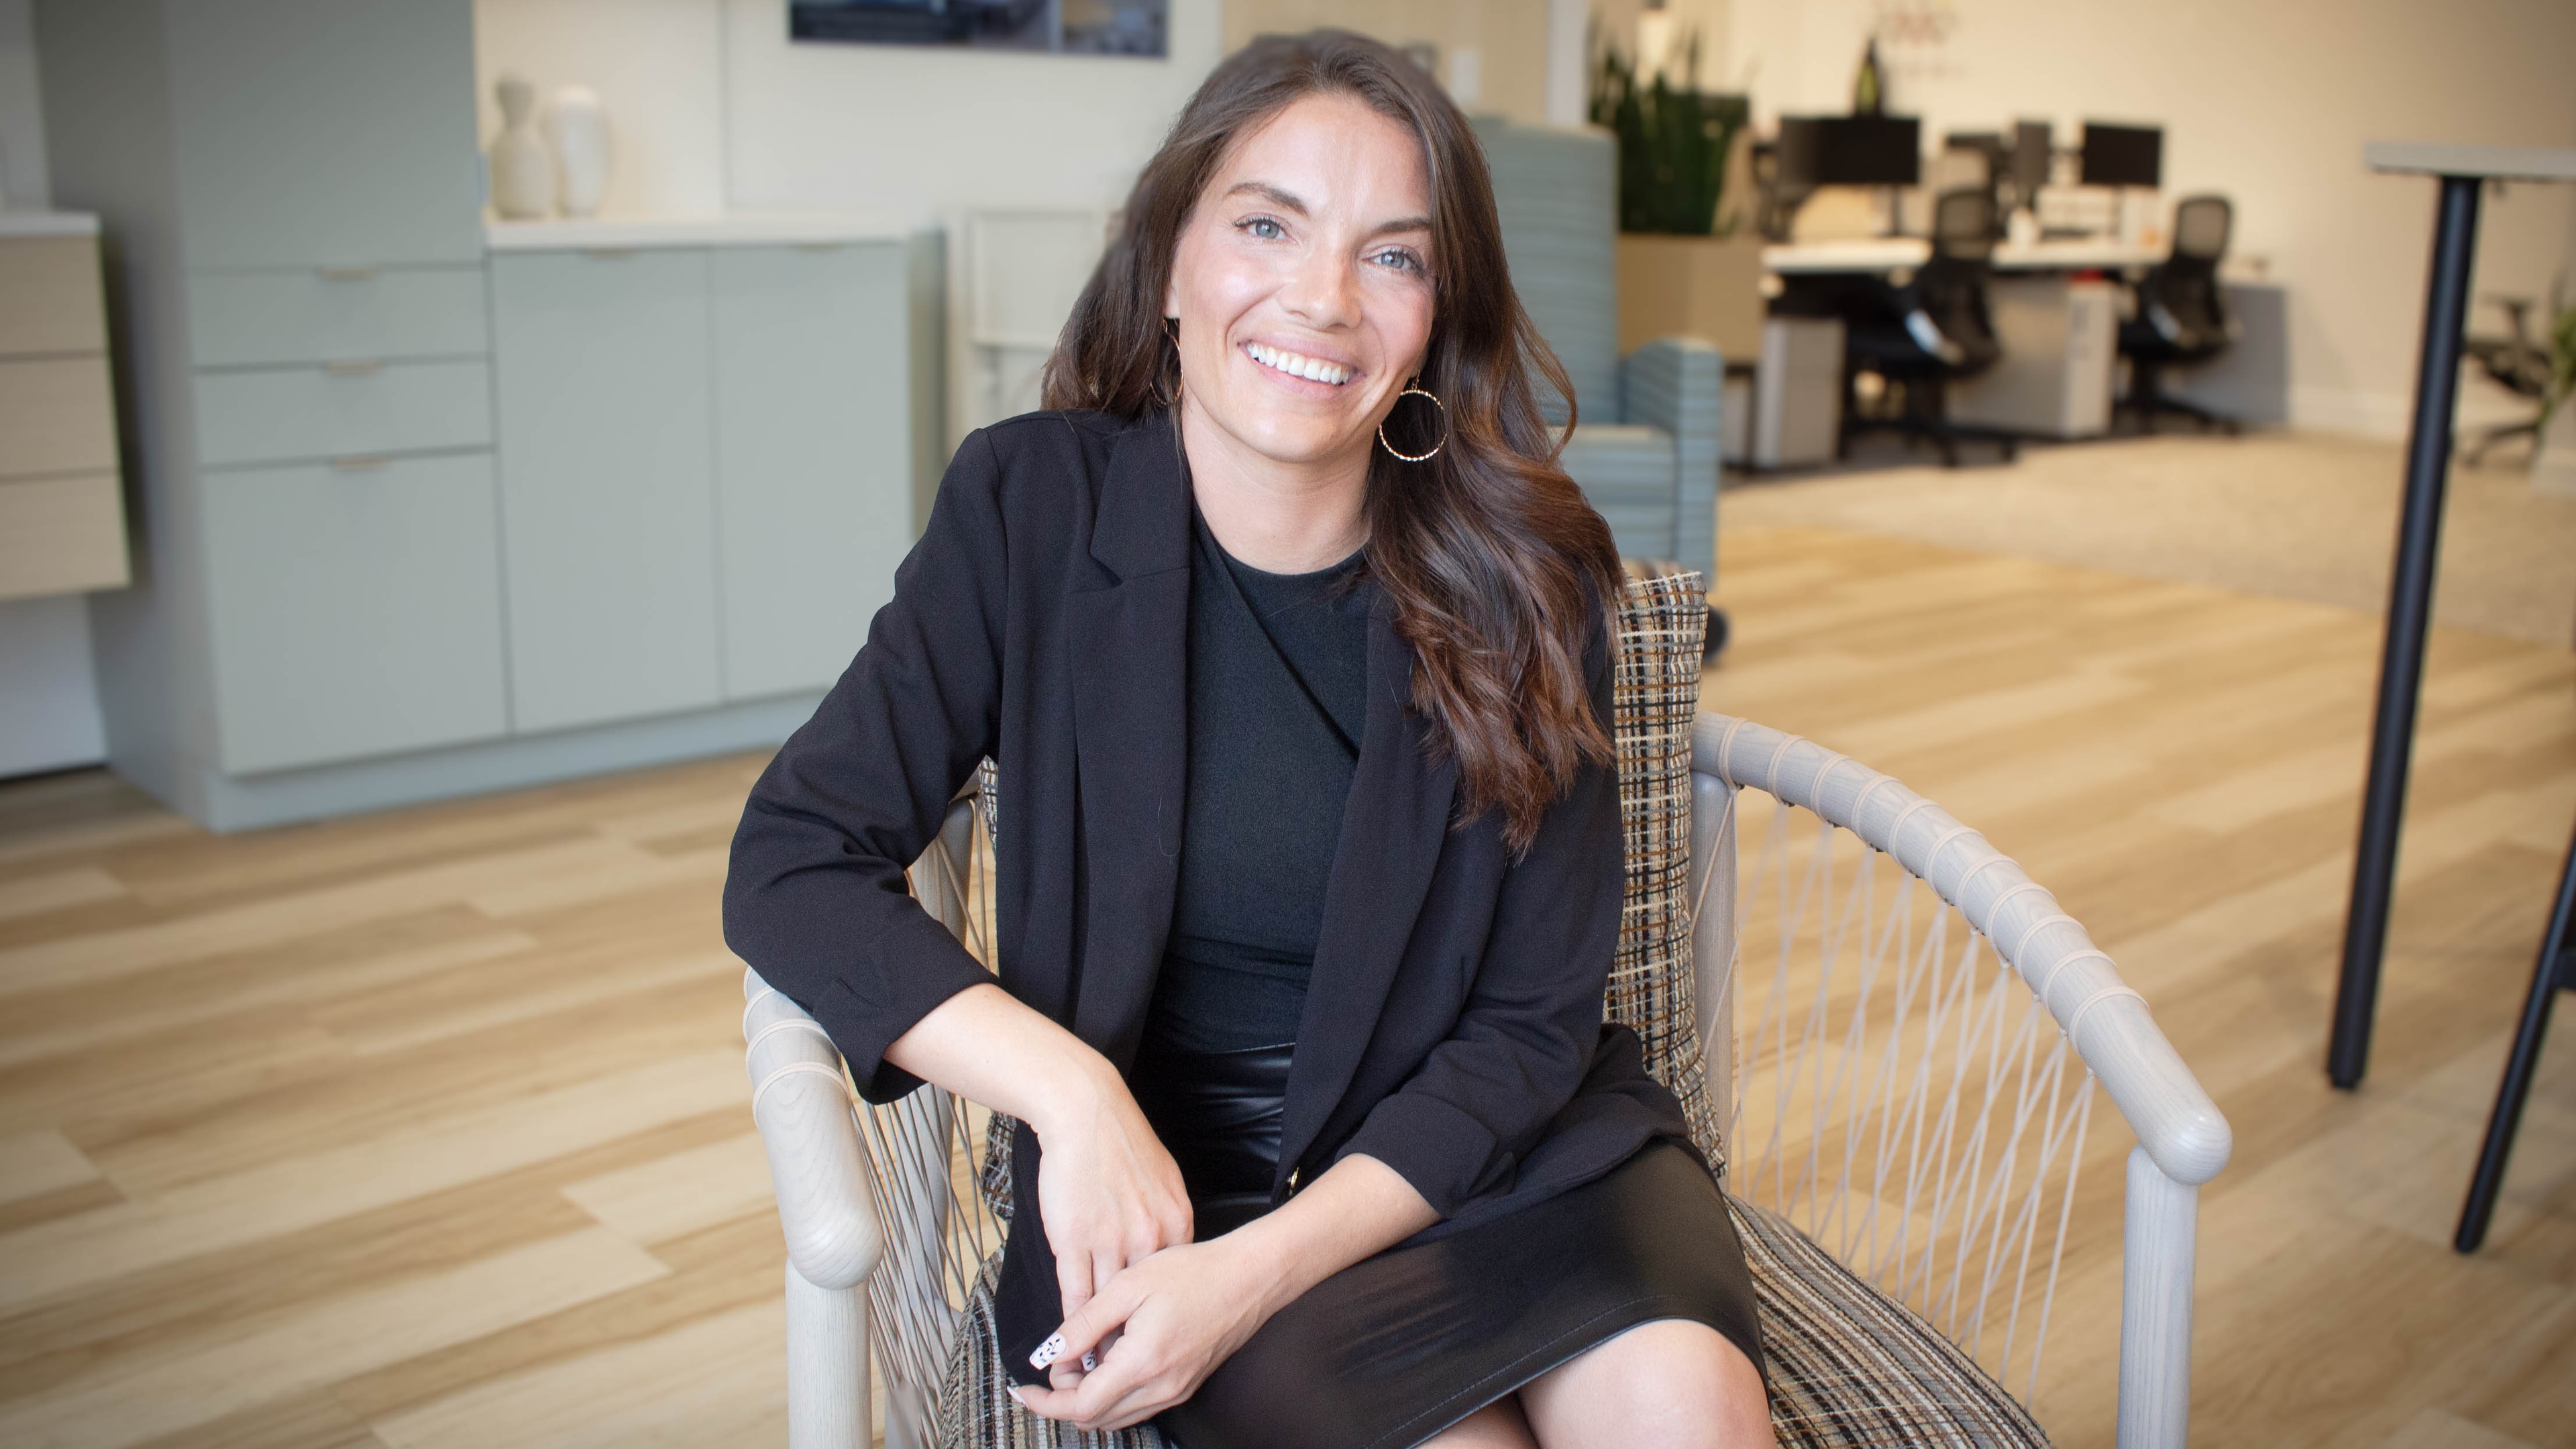
Founder & Principal Consultant, Jack-IT Consulting
Technology Strategy · AI Advisory · Business Operations · Executive Leadership
Jacquelyn Mosier is the Founder and Principal Consultant of Jack-IT Consulting. With a background in national sales leadership, team development, and business operations, she built Jack-IT on a straightforward premise: technology decisions should start with the business, not the software. She works directly with leadership teams to evaluate investments, identify operational gaps, and build strategies that connect people, processes, and systems before recommending what comes next.